Latest Version
September 15, 2026
Cisco Systems, Inc.
BUSINESS
Android
70
Free
com.cisco.secureclient.zta
Report a Problem
More About Cisco Zero Trust Access – Secure Remote Connectivity
What is Cisco Zero Trust Access?
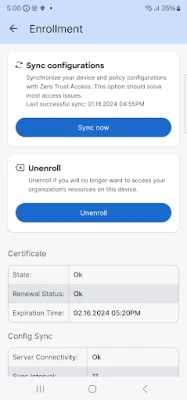
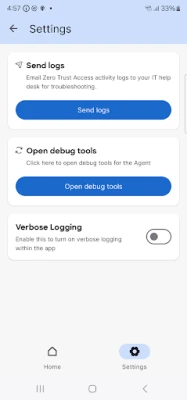
Cisco Zero Trust Access is a mobile client that enables organizations to extend their security perimeter to Android devices. By leveraging Cisco’s Zero Trust model, the app creates a secure, encrypted tunnel that connects a user’s device to the corporate network only when the appropriate policies are satisfied.
Main capabilities
- Policy‑driven access – Connections are granted based on identity, device posture, and contextual factors such as location or time.
- Device‑level encryption – The app uses Android’s VpnService framework to build a protected tunnel that isolates corporate traffic from other network activity.
- Least‑privilege enforcement – By default, access is denied; only explicitly approved applications and resources become reachable.
- Seamless user experience – Once configured by an administrator, users launch the client and are connected without repeatedly entering credentials.
How it works
When a user opens the client, it authenticates against the organization’s Cisco Secure Access backend. After successful authentication, the backend evaluates the user’s profile, device compliance status, and any additional risk signals. If the request meets the defined policy, the app establishes a VPN tunnel using Android’s native VpnService API. All traffic destined for corporate resources is routed through this tunnel, while internet traffic continues to use the regular network path.
Practical uses
Enterprises that require remote workers to access internal applications—such as intranet portals, file servers, or custom business tools—can rely on Cisco Zero Trust Access to enforce strict access controls without sacrificing usability. The client is especially useful for:
- Employees working from home or on the road.
- Contractors who need temporary, tightly scoped access.
- Teams that handle sensitive data and must comply with regulatory requirements.
Installation information
The application is distributed as a free download. Installation follows the standard Android process: download the APK from a trusted source, tap the file, and follow the on‑screen prompts. Because the client uses the VpnService API, Android will request permission to set up a VPN connection; users must grant this permission for the app to function.
Compatibility and requirements
The app is designed for devices running a recent version of Android that supports the VpnService framework. Specific version numbers are not published, but the client will not install on devices lacking the required system APIs. Organizations must have an active Cisco Secure Access subscription; the client alone does not provide Zero Trust capabilities.
Things to know before installing
- Configuration is performed by your IT administrator. You will need the server address and any required authentication tokens.
- The app does not replace a full‑featured VPN client; it is purpose‑built for Cisco’s Zero Trust architecture.
- Because the client routes only corporate traffic through the tunnel, personal browsing remains on the regular network, preserving bandwidth for non‑work activities.
Who may find it useful?
Any organization that has adopted Cisco’s Zero Trust security framework and needs a lightweight Android client for remote access will benefit. This includes large enterprises, government agencies, and midsize companies with distributed workforces.
Frequently asked questions
Do I need a Cisco account to use the app?
Yes. Access is granted only after your identity is verified against the Cisco Secure Access service managed by your organization.
Can the app be used with other VPN solutions?
No. Cisco Zero Trust Access is tightly integrated with Cisco’s backend services and is not intended to work with third‑party VPN providers.
What happens if my device falls out of compliance?
The client will automatically disconnect the tunnel and prevent further access until the device meets the required security posture.
Rate the App
User Reviews















Popular Apps










 Games
 Entertainment
 Communication
 E-mail
 Security
 Tools
 Media
 Internet
 Finance
 Design
 Education
 Android Firmwares
 Travel & Local
 Android
 Windows
 Linux